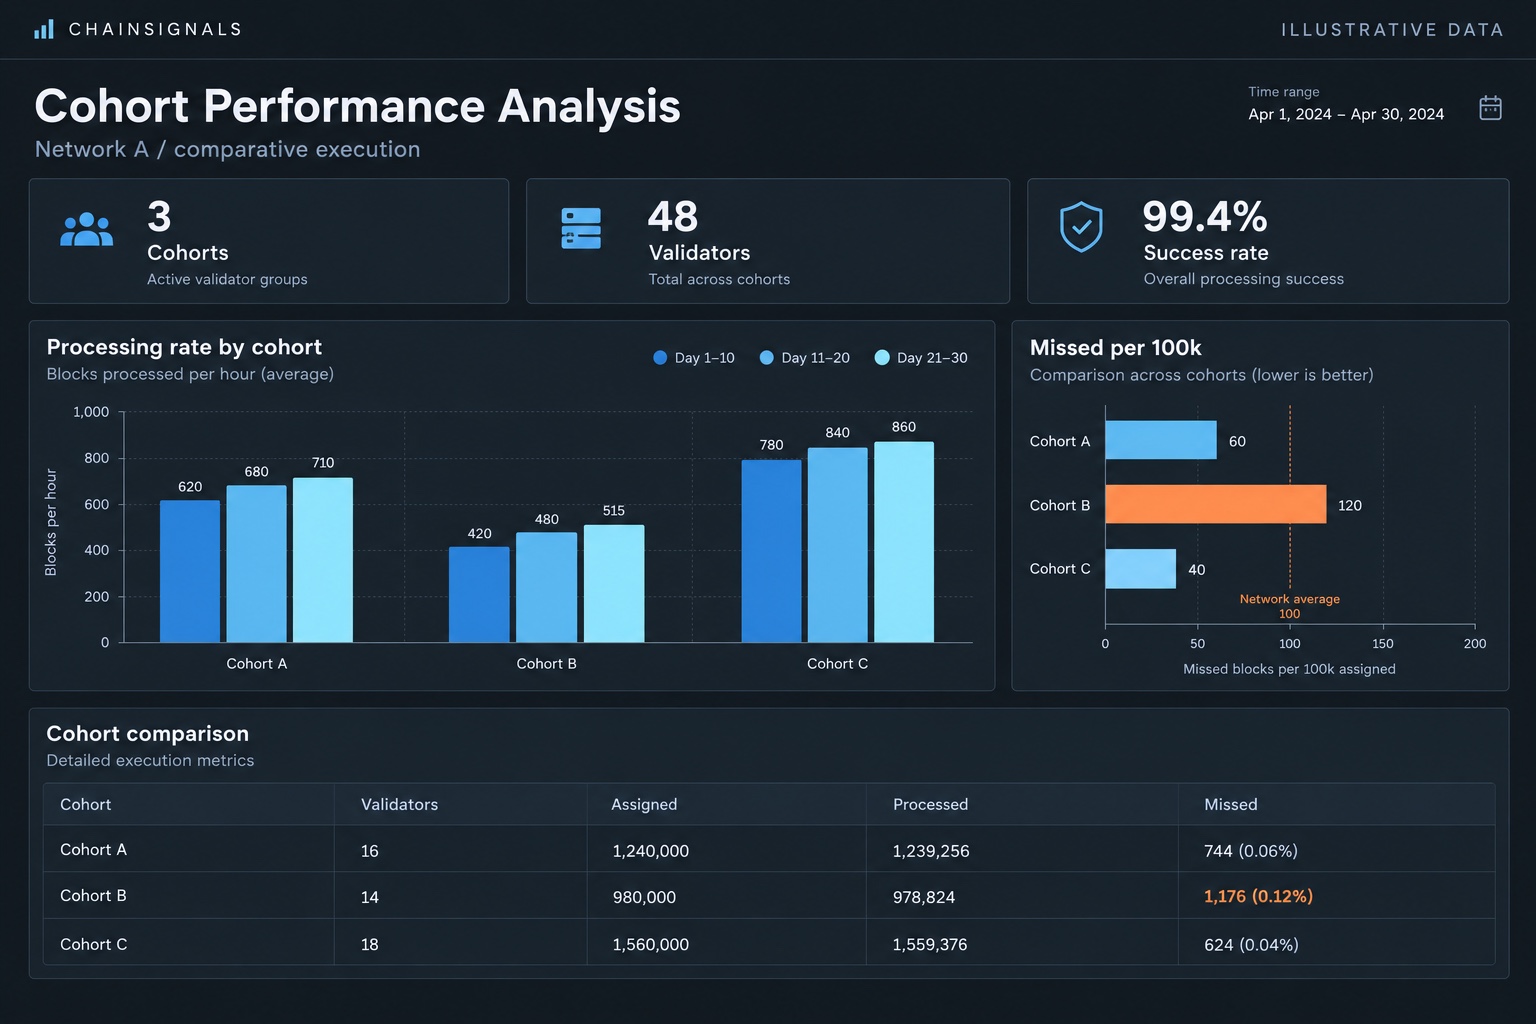
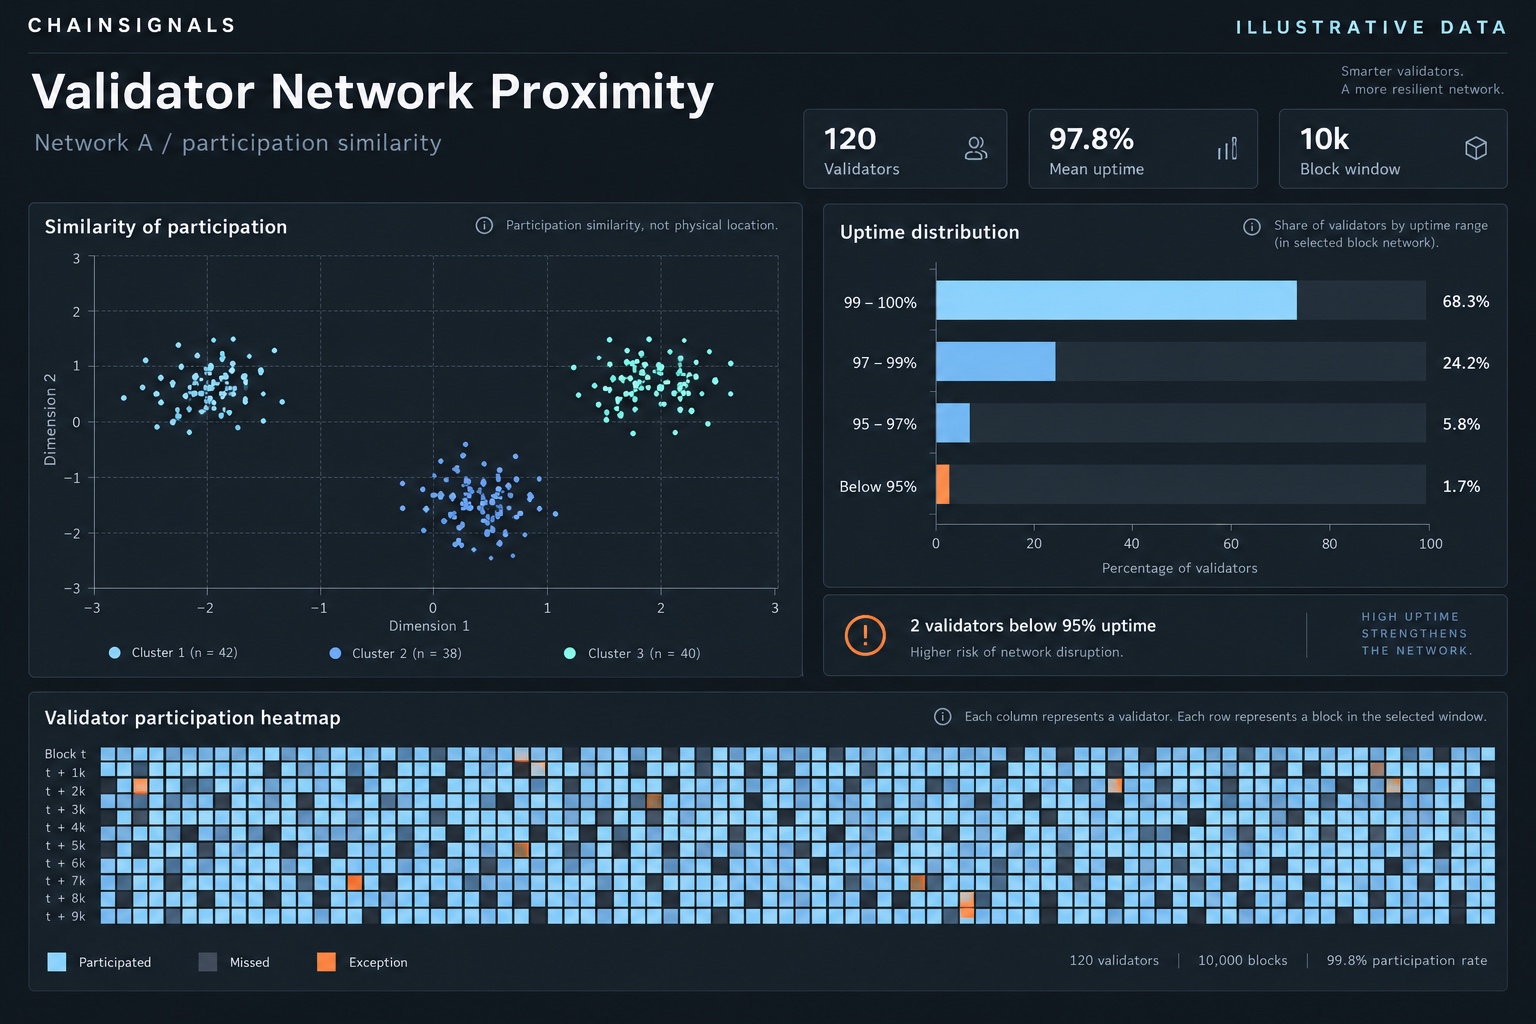
Security & infrastructure
Security at every layer.
Resilience by design.
Our operating model combines dedicated hardware, isolated signing, controlled network access and continuous observability. Each layer has a clear role, boundary and recovery procedure.
HARDWARE
Dedicated capacity
Bare-metal infrastructure with high-performance CPUs, NVMe storage and capacity planned around consensus workloads. Performance checks inform upgrades and configuration changes.
Bare metal / NVMe / Benchmarking
NETWORK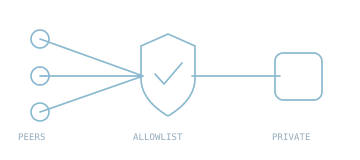
Restrict the attack surface
Sentry and private-network patterns separate public peers from sensitive workloads where supported. VPN access, firewall allowlists and hardened SSH keep management access controlled.
Sentries / VPN / Access control
KEYS
Protect consensus signing
Isolated remote signing with TMKMS where supported, restricted signer access and hardware wallets for administrative operations. Failover verifies signing state before a standby is activated.
Key isolation / KMS / Signing state
OBSERVABILITY
See issues early
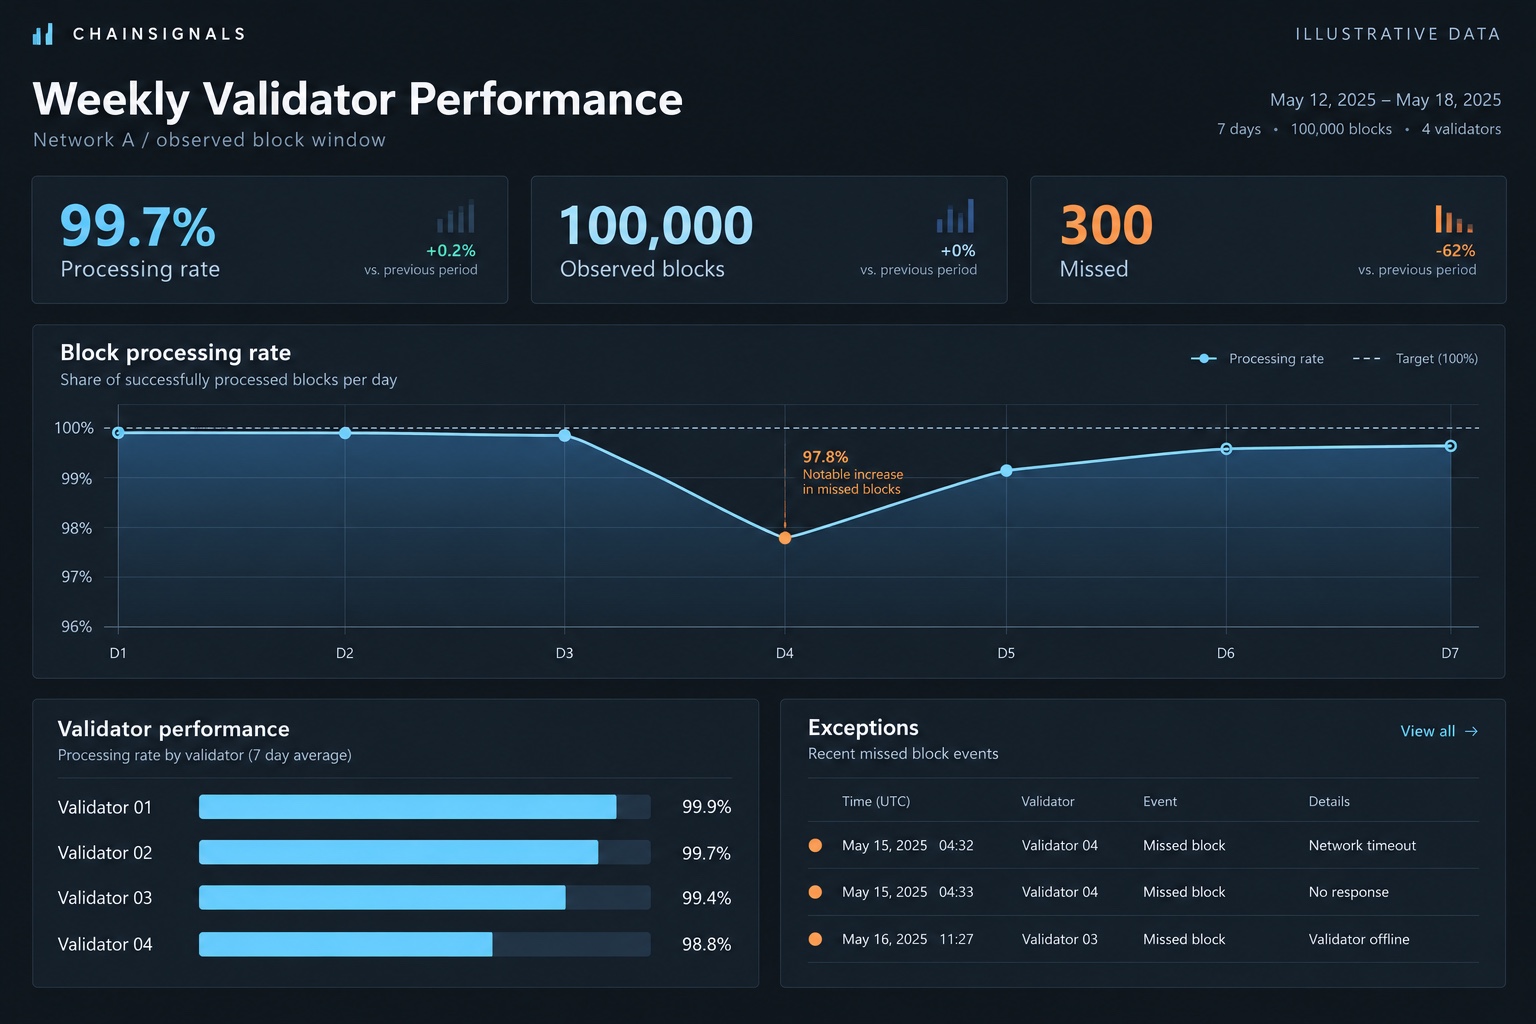
Prometheus and Grafana track consensus, signing latency, peers and host resources. Automated alerts and on-call coverage turn deviations into investigation and response.
Prometheus / Grafana / Alerting
CHANGE CONTROL
Make changes repeatable
Ansible and Terraform support reproducible environments. Versioned configurations, isolated builds and staged upgrades make deployment and recovery easier to inspect.
Infrastructure as code / Staging
RECOVERY
Recover with discipline
Validated backups, restore exercises and documented runbooks support recovery. Synchronization and signing-state checks come before validation resumes.
Backups / Restore tests / Runbooks

 View example ↗